| ▲ | rudolftheone 7 hours ago |
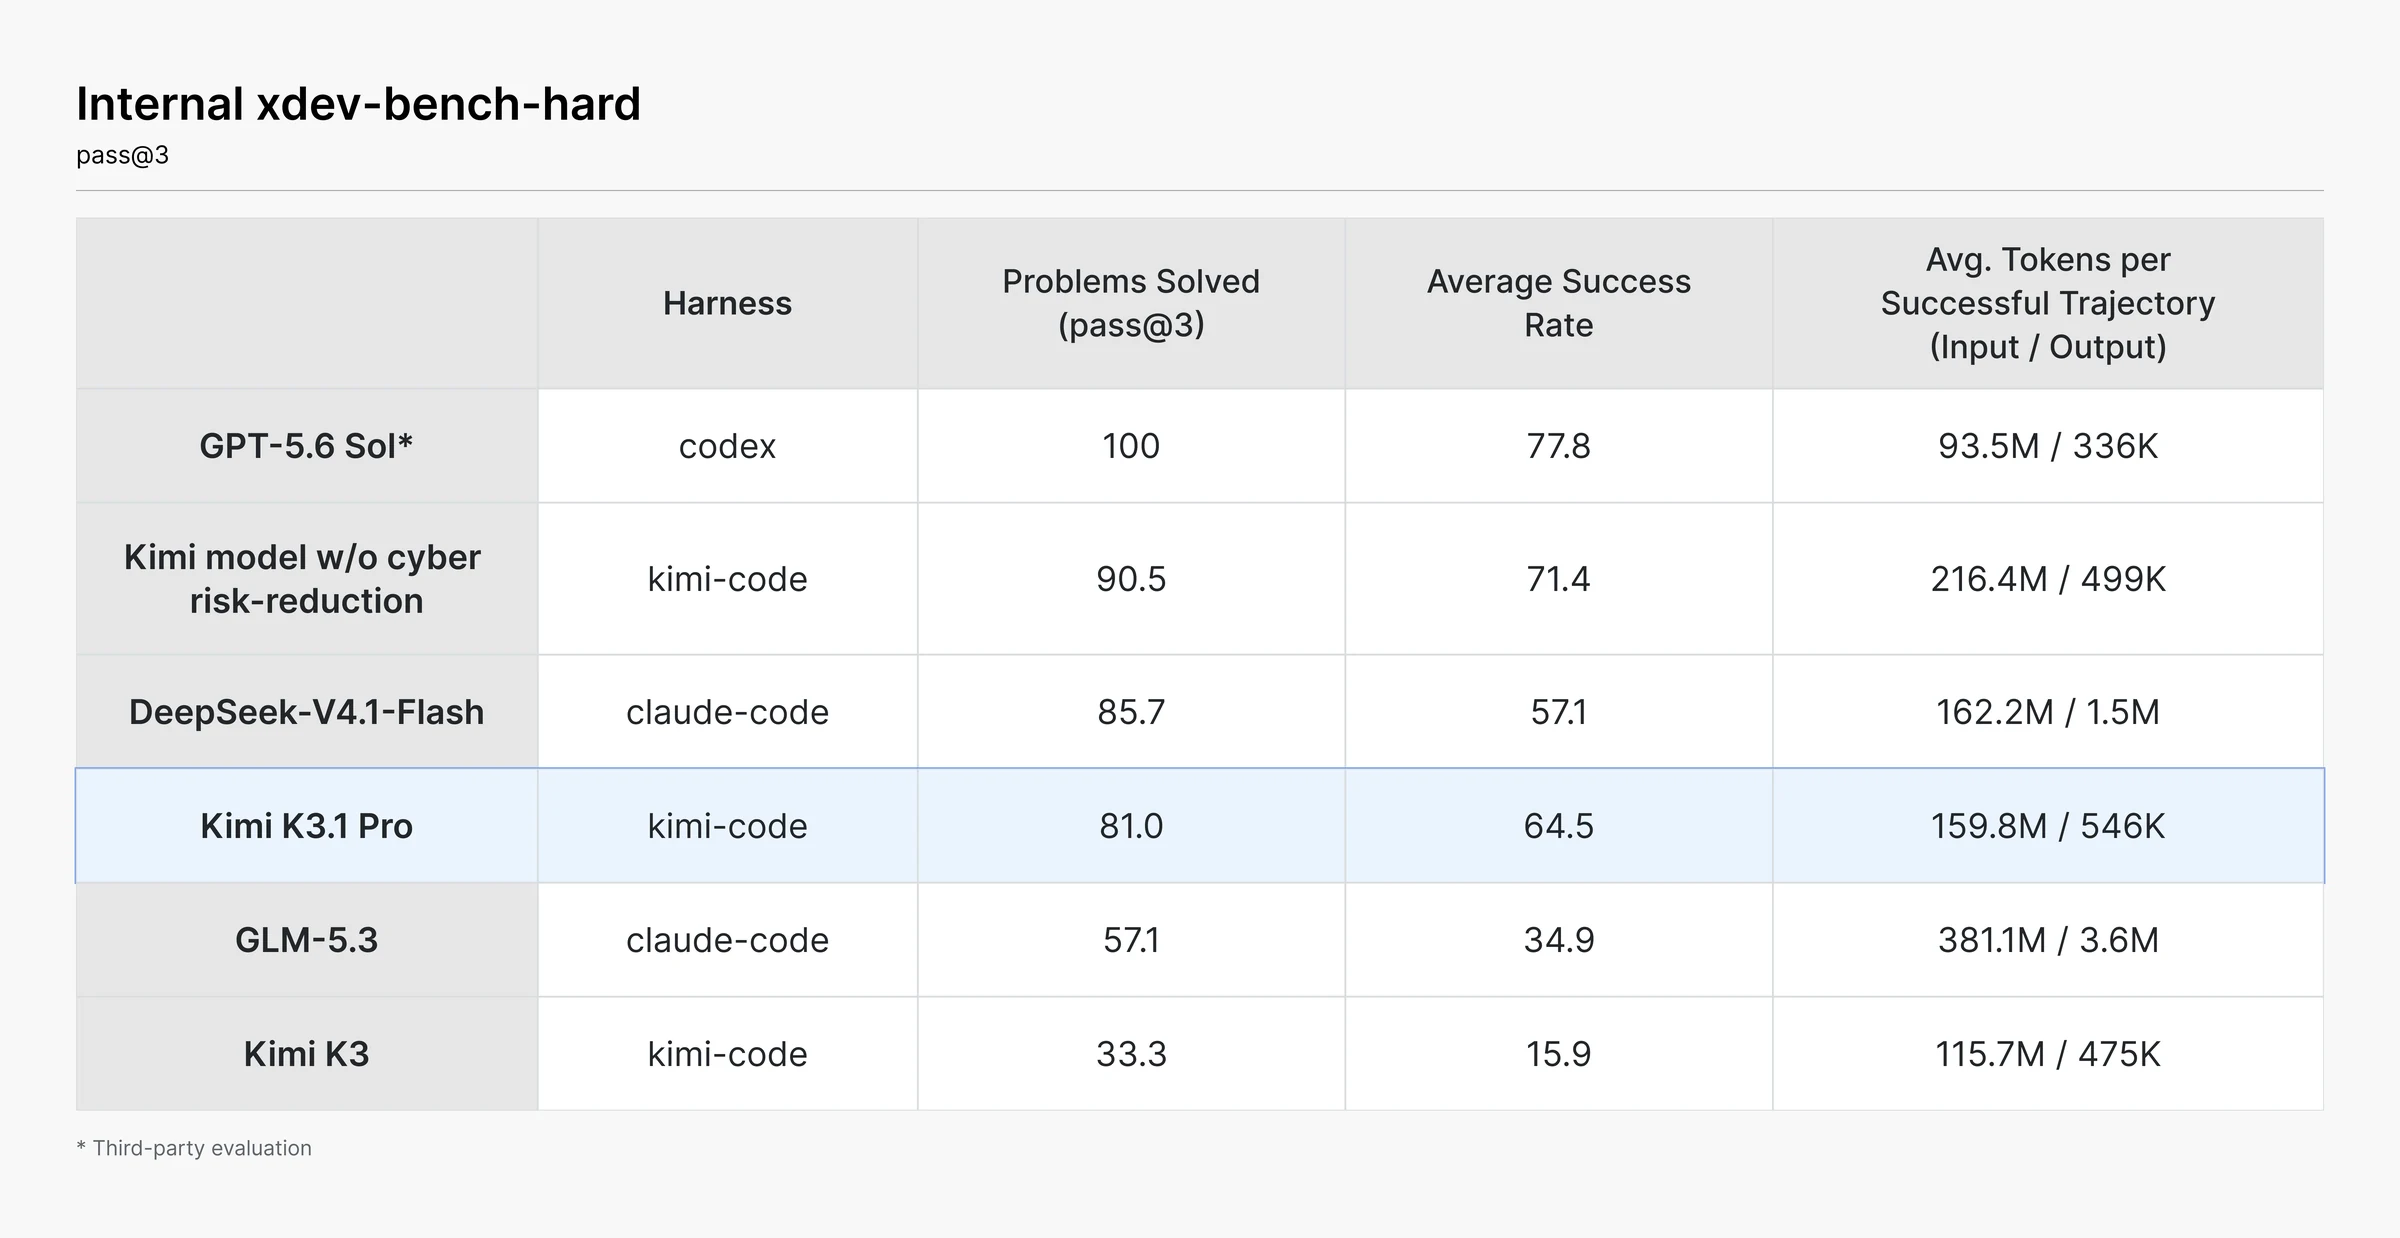
| That's something which caught my attention: > First, we aim not to release open weights that would extend the absolute frontier of cyber capability. K3.1 Pro's offensive cyber capability is, by design, below what our pipeline can produce, and remains behind that of frontier proprietary models. Second, we intend to progressively raise the cyber capability available in open weights. So they admit that they could do more, but they won't? |
|
| ▲ | NitpickLawyer 6 hours ago | parent | next [-] |
| > So they admit that they could do more, but they won't? Yeah, there's another paragraph: > Identifying and removing cyber-related data. During development, we observed vulnerability research performance improving steadily as post-training scaled. Tracing the source of this trend, we found that cyber-related content was embedded within the general mid-training corpus, and cyber-related tasks were present in the RL environment mix — a natural byproduct of training on broad data. In preliminary experiments on internal models, we found that without data removal at either the mid-training or the RL stage, downstream cyber capability would increase substantially. These findings gave us a concrete lever for control. For the open-weight release of K3.1 Pro, we identified and removed cyber-related data from both training stages, while retaining the general-purpose coding tasks needed for model usefulness. We will continue to apply appropriate controls at every training stage, of which cyber-related data identification and restriction is one example. (emphasis mine) It's clear that cyber is a touchy subject right now. But it's also clear that RL works on it, because it's highly verifiable. So smaller models are going to become very interesting, because they can be fine-tuned later to cover this field. |
| |
| ▲ | neuronexmachina 4 hours ago | parent | next [-] | | I'm betting this is related to China's Announcement No. 48 last week about AI export controls, since releasing an open-weight model is effectively export: https://www.jdsupra.com/legalnews/china-proposes-new-export-... > Prohibited: high-performance detection technologies used to counter cross-border data transmission security risks, including deep-synthesis forgery detection (266401J); AI cyber offensive capability technologies, such as malicious code generation and mutation, automated mass generation and distributed large-scale deployment of anti-detection variants (266402J); large models trained using China’s Core Data (266501J); and high-performance AI agents designed for highly sensitive scenarios, such as critical information infrastructure, national defense and core government affairs (266502J). | |
| ▲ | yorwba 6 hours ago | parent | prev | next [-] | | They also show scores for a "Kimi model w/o cyber risk-reduction" https://statics.kimi.ai/kimi-blogs/kimi-k3-1/20261023/xdev-b... Presumably State Security will get access to that on request. | |
| ▲ | dotancohen 4 hours ago | parent | prev | next [-] | | > It's clear that cyber is a touchy subject right now.
And that's why we need models that understand "cyber" or application and data security. The offensive models are powerful, and they are in the hands of script kiddies now. The models writing our software and designing our cloud infrastructure had better understand these issues as well, just to avoid coding in vulnerabilities. | |
| ▲ | fartfeatures 5 hours ago | parent | prev | next [-] | | I think this is misguided. Considering how much code is AI written these days do we really want LLMs writing insecure code because we lobotomised them? | | |
| ▲ | MattDaEskimo 5 hours ago | parent | next [-] | | I think it's political. Certain companies are exploiting as much as possible to push the boogeyman of AI for regulation. | | |
| ▲ | echelon 4 hours ago | parent [-] | | It's exactly this. If the "scary Chinese open weights models" can do "dangerous cyber", then we might see regulations spring up against open weights sooner than later. I hate Anthropic and OpenAI. As companies and leadership, anyway. Dario and Sam are 100% to blame for this. They're trying to turn us all into jobless slaves, sex workers, and Squid Game pawns. The only good future is open weights. They're trying their damnedest to keep us under boot. I hope the Chinese companies (and I say this as a patriotic American) slay these two companies and destroy their moats. In my mind, the two most dangerous people in the world are Dario and Sam. We need open weights to win. | | |
| ▲ | m348e912 4 hours ago | parent | next [-] | | > They're trying to turn us all into jobless slaves and sex workers. Speak for yourself, I don't think there is a market for many of us as the latter. | | |
| ▲ | lapetitejort an hour ago | parent | next [-] | | Don't be too hard on yourself. There's someone out there for everyone. The problem is they don't pay well | |
| ▲ | echelon 4 hours ago | parent | prev [-] | | Let me edit my comment :) |
| |
| ▲ | mebrainmush 2 hours ago | parent | prev | next [-] | | Please enjoy some time out in the nature, and chill out. These times are not ideal but what can we do other than just take it as it comes? All the hate and rage is not good for your health. | |
| ▲ | Hammershaft 3 hours ago | parent | prev | next [-] | | Why do you think Dario is dangerous? I think he's genuine on the dangers of AI capabilities moving faster than AI alignment. | | |
| ▲ | qlte an hour ago | parent | next [-] | | Which is a great example of what makes him dangerous: with the exception of Sam Altman he's arguably the single person most responsible for the current capabilities arms race. Anthropic has pushed the frontier harder and faster than OpenAI or anyone else in the last few years. Beginning with Anthropic's founding to quickly raise huge amounts of cash with a pitch to investors to rapidly leapfrog ChatGPT in scale, and culminating with Mythos/Fable which carved out a whole new tier of super models. He's always talked big about Anthropic prioritising safety and their "Responsible Scaling" but his words just simply don't align with reality while they keep going bigger, faster, until only OpenAI could briefly and half-heartedly claim near parity at the top (while cutting corners in safety because the existential threat to their market position is far more pressing to any corporation than some abstract risk for humanity). Whether it's wilful cognitive dissonance, cynical opportunism, financial greed or something else, that kind of self-assured moral superiority paired with his real world record of self-interested decision making for Anthropic's market position is a big red flag. | |
| ▲ | smashed 3 hours ago | parent | prev [-] | | Because his solution is to block competition and capture all the market through regulation. | | |
| ▲ | sroussey 3 hours ago | parent [-] | | VCs will teach companies all about the wonders of regulatory capture! |
|
| |
| ▲ | felixgallo 3 hours ago | parent | prev | next [-] | | Sam, I'll grant you, is probably among the top 10 most dangerous, but Dario? The only thing he's done to piss people off is to predict, correctly, that releasing too-powerful models too-quickly would cause havoc and chaos. This prediction actively hurts his company! It actively harms his chances of a huge exit! It actively raises the probability that Anthropic and OpenAI get nationalized and treated in the same way as, for instance, the nuclear program! By comparison, do you think the Chinese models are going to be trained in such a manner that you enjoy the society that results? What makes you think that? | | |
| ▲ | echelon 3 hours ago | parent [-] | | > do you think the Chinese models are going to be trained in such a manner that you enjoy the society that results? I don't need government minders. I'll take the models and live free. |
| |
| ▲ | pixl97 4 hours ago | parent | prev [-] | | >I hope the Chinese companies (and I say this as a patriotic American) slay these two companies and destroy their moats. China cares about about stability way more than the US even, they aren't going to be big on AI models upsetting the governments power, and mass cyber attacks could do that. At the end of the day we are going to have to realize AI is both dangerous and governments are going to control it. Worse if you start making and releasing your own dangerous models the 4chan party van is going to visit you. | | |
| ▲ | echelon 4 hours ago | parent [-] | | > At the end of the day we are going to have to realize AI is both dangerous and governments are going to control it. Your thinking is dangerous. Do you work for Anthropic? AI is dangerous when these powers are being hobbled up by the select few. These systems threaten to put us all out of work. I refuse to be a slave to a company or a government that is taking away our livelihoods, scraping up our earnings potentials, then seeking to muzzle us and put us in jails with no rights. I would rather burn down all of tech than have AI be owned by the elites. Your thinking is a threat to all of our liberties. | | |
| ▲ | pixl97 3 hours ago | parent [-] | | >I would rather burn down all of tech than have AI be owned by the elites. Then you better get your torches out now. >I refuse to be a slave to a company or a government that is taking away our livelihoods Don't worry, governments are fervently working on AI drones to take away your life when you get really upset about this. Oh, and they are also working at AI to detect when you write all this online, and track you down then monitor you on things like flock cameras. As they say, you'll be the first with your back against the wall when the revolution comes, I likely will be beside you for being too subversive. >AI is dangerous when Incorrect, AI is just dangerous. It doesn't matter who has it. The more powerful it becomes the more dangerous it gets. So, as you can tell I am an AI doomer. ---- Now, don't get me wrong, I want freedom for me, I want freedom for other people. I do not believe the technologies we're developing are conductive to having any freedom at all. Hell, if we're lucky we'll be slaves instead of all of us dead, including the select few. >Your thinking is a threat to all of our liberties. Lol, now this is kind of funny. "I want freedom to think whatever I want, but you, you shouldn't think like that!". Careful or you'll max out your irony meter. Anyway, "My kind of thinking" is just next ____ prediction. I see what is happening in the world around us, and based on the shape of that probability I see what is going to happen. No, you and I are not getting unlimited AI to do whatever we want. Yes, governments are going to lock down the shit out of AI for end users. Yes, governments are going to declare advanced LLMs munitions. Balls in your court, better think of what your next move is. |
|
|
|
| |
| ▲ | 4 hours ago | parent | prev | next [-] | | [deleted] | |
| ▲ | zer00eyz 5 hours ago | parent | prev [-] | | Anthropic: Touch too much security stuff and we ban you, and keep your money. Kimi: We took out the worst of it so have at it for free. Everyone else: Back to my ablated model on openrouter for 1/10th the price where I can brute force issues. | | |
| ▲ | jacquesm 5 hours ago | parent | next [-] | | Ablation only works to remove stuff added in post training, if the training data does not contain the material then ablation will do nothing. | |
| ▲ | anonymousDan 5 hours ago | parent | prev [-] | | Which ablated model do you recommend for this? | | |
|
| |
| ▲ | sheepscreek 6 hours ago | parent | prev | next [-] | | It’s not much of a deterrent to a motivated organization. They are basically saying that models themselves are already capable. If you fine tune them with some cyber security tasks, that should make them potent. :-/ | |
| ▲ | vessenes 6 hours ago | parent | prev [-] | | Classic “rules for thee and not for me.” Agreed that this could be reinjected later. Makes me think of neo in the matrix: “I know zero days.” “Show me.” | | |
| ▲ | zozbot234 6 hours ago | parent | next [-] | | What "rules"? They don't have to post-train the model on anything specific, it's their judgment call. | | |
| ▲ | vessenes 5 hours ago | parent | next [-] | | The "rule" here is, if you read the disclosure carefully, that they have cyber trained models in house. But you do not get them, you only get the non-cyber models. | |
| ▲ | mlmonkey 6 hours ago | parent | prev [-] | | Post-training _is_ a part of the whole training regime. |
| |
| ▲ | pixl97 4 hours ago | parent | prev | next [-] | | Governments also control who owns tanks and missiles. Do you think that going around making cyber weapons isn't going to get you buried in a shallow grave? | |
| ▲ | 5 hours ago | parent | prev [-] | | [deleted] |
|
|
|
| ▲ | mrandish 5 hours ago | parent | prev | next [-] |
| With frontier competitors and the U.S. govt actively pushing "concerns" about Chinese models, Kimi including this statement on "offensive cyber capability" seems like smart defense. Models are opaque and training details are trade secrets, so whatever they did might be negligible or significant and no one can tell. This bit is also artfully done: > "below what our pipeline can produce, and remains behind that of frontier proprietary models." Like Ant and OAI, they've realized vaguely claiming to have nerfed their latest model to an unspecified degree not only looks 'good guy' prudent, it provides a built-in excuse when a model fails. |
| |
| ▲ | mirekrusin 5 hours ago | parent [-] | | I'm not sure if not doing RL capability gain on offensive cybersecurity can be really called "nerfing"? They're not post training it to lose capabilities/censor them – they just don't spend training time on this topic, which sounds like a great idea. It doesn't mean model can't do it, it just means it's less good at it; -10% on benchmark feels like a great result and overall approach to pace it. | | |
| ▲ | mrandish 3 hours ago | parent [-] | | > I'm not sure if not doing RL capability gain on offensive cybersecurity can be really called "nerfing"? I concede that term can carry overly broad connotations. |
|
|
|
| ▲ | scottyah 7 hours ago | parent | prev | next [-] |
| Or it's a cop out. I could totally outrun Usain Bolt, but by design I don't push to set new World Records. I will increasingly show faster times though. |
| |
| ▲ | locknitpicker 4 hours ago | parent | next [-] | | > Or it's a cop out. I could totally outrun Usain Bolt, but by design I don't push to set new World Records. The benchmarks show Kimi K3.1 Pro outrunning practically all models. It's weird to hear someone like you accusing them of making up excuses for not lagging behind in discussions on how they are ahead of the pack. | |
| ▲ | stalfie 7 hours ago | parent | prev [-] | | Well, in the publication they claim to have identified specific cybersecurity post training tasks that nerfed capabilities when they removed them, which seems like a reasonable methodology. Seeing as no one besides blackhats want frontier cybercrime capability to be open source, this seems like a very sensible thing to do. So they have published a reasonable means, and they have a motive. I'd put my money on "probably true". | | |
| ▲ | InsideOutSanta 6 hours ago | parent | next [-] | | > Seeing as no one besides blackhats want frontier cybercrime capability to be open source Sure. The problem is that there is no practical difference between "cybercrime capability" and "cybercrime defense capability." All of my PRs go through an adversarial security review by GLM-5.3, because it's the only smart-enough model with a good understanding of cybersecurity issues that won't regularly refuse the job. Removing that ability from frontier models helps nobody except cyber criminals. | | |
| ▲ | stalfie 3 hours ago | parent [-] | | I'm not sure I follow. Let's say that GLM remains the frontier of open source cyber capabilities because Kimi is nerfed. Your situation, and the situation of your attackers, remain exactly the same. You run GLM to audit your code, they do the same looking for exploits. Let us say that un-nerfed Kimi was released, and it turns out to be at the absolute frontier of cyber capabilities, Mythos 5.5 level, a step ahead of anything else. What now? Well now your situation is exactly the same as before, just that auditing and hacking got more expensive. You run a Kimi security audit, they do the same to try to pwn you. However, now the cabal of Linux kernel defenders with secret access to Mythos 5.5 all of a sudden have no advantage, where before they used to have one. And even worse now they are in a literal race to be the first ones to find every bug that Kimi is capable of finding, and patching it yesterday. So for you, this makes no difference in practice, your capabilities are not elevated, and neither are those of the attackers. The only result of the other scenario is an overall defender disadvantage. |
| |
| ▲ | ApolloFortyNine 6 hours ago | parent | prev | next [-] | | The problem is, as anyone trying to address security concerns in claude can attest to, the guardrails trigger even when trying to address real bugs. Good cyber defense requires an understanding of the offense. How you avoid the "fix my code" attack, the code being someone else's code, I do not know. But nerfing the model doesn't seem like the best path forward either. | | |
| ▲ | zozbot234 6 hours ago | parent | next [-] | | This is not about guardrails, it's just not post-training the model on tasks that specifically relate to cyber-offense. It's a very lightweight intervention, and it makes the model less of a target for bad actors. | |
| ▲ | tough 6 hours ago | parent | prev [-] | | claude code "auto-mode" uses a smaller sonnet-like model for classifying, which means it's basically dumb, and the harness biases it into denials |
| |
| ▲ | tkz1312 5 hours ago | parent | prev | next [-] | | I am a defender, and I really really want to have access to high quality models that are good at finding vulns and hacking. Leaving them in the hands only of government agencies and orgs with enough resources to do extensive training / fine tuning seems like the absolute worst possible case for the future security of global software systems. | | |
| ▲ | stalfie 4 hours ago | parent [-] | | Well, and I am genuinely curious here, wouldn't defender and attacker capabilities being accessible equally by both parties be objectively worse than having a limited amount of privileged defenders? Of course, you could have every piece of code go through an adversarial audit before it's pushed, but in an equal world you would have to always devote as much or more resources to this as your attackers. And historically speaking people just don't do this in practice. In the scenario where only "verified" defenders get access to the best cyber capabilities, unverified plebian defenders and blackhats are on the same level exactly as described above, there's just also a few defenders that get to run things on godmode. So to me, it seems that the only result of frontier cyber capabilities is removing a defender advantage. Although that advantage is not for everyone, it can only exists as long as capabilities are unequally distributed. Am I missing something? | | |
| ▲ | Avamander 3 hours ago | parent | next [-] | | > Well, and I am genuinely curious here, wouldn't defender and attacker capabilities being accessible equally by both parties be objectively worse than having a limited amount of privileged defenders? Well, not really. Because those privileged defenders will never be able to predict what needs defending. So we have a few privileged "defended" places and the rest is left for privileged attackers to plunder. | | |
| ▲ | stalfie 3 hours ago | parent [-] | | Privileged attackers?? So that would be career cybersecurity experts with Project Glasswing/Daybreak/Googlewhatever access, using it to perform actual attacks? Because that's what privileged means in this context. Access to frontier models not available to the public. | | |
| ▲ | Avamander 3 hours ago | parent [-] | | > So that would be career cybersecurity experts with Project Glasswing/Daybreak/Googlewhatever access. Yes. You really think access those models will not be given for offensive operations in each country? Of course they will be. | | |
| ▲ | stalfie 2 hours ago | parent [-] | | Well, seeing as Claude literally snitches on everyday people planning murder and Houthis building rockets I would assume that every user in project Glasswing is heavily and very effectively monitored. I have to admit that I genuinely do not think that what you're hypothesizing is happening right now. I would bet good money that the amount of people with Glasswing access doing actual Blackhat work is currently zero. Perhaps in the future this will change, but even if that is the case, that's still a win for the defenders. Having a time advantage, even for a few months, is still a win. Edit: Actually, the CIA/FBI/NSA/Etc.. does probably have access and are probably trying to hack Iran and so forth, so my comment above is probably technically wrong in that respect. | | |
| ▲ | Avamander 2 hours ago | parent [-] | | > I would bet good money that the amount of people with Glasswing access doing actual Blackhat work is currently zero. I think it's not "blackhat" in that sense because it's officially sanctioned. Same goes for equivalent models overseas. The only thing these embargos achieve is giving massive nations a huge advantage, but leaves the average country and person exposed. | | |
| ▲ | stalfie 2 hours ago | parent [-] | | I edited my comment above before realizing this is what you meant. And its a valid point I concede. Still, I disagree that advantaging this activity is the only thing these embargoes achieve. I would argue that they legitimately also give the Linux kernel, cURL and so on an advantage. And as long as that is true, this still makes it an overall win in my books, even if it also enables officially sanctioned offensive activities. I'm not a US citizen, but I would still rather get pwned by the CIA than both the CIA and Shinyhunters. |
|
|
|
|
| |
| ▲ | tkz1312 3 hours ago | parent | prev [-] | | Because the people I want to defend against includes those with enough resources to train and fine tune models with strong offensive capabilities themselves. | | |
| ▲ | stalfie 2 hours ago | parent [-] | | Ah, now that's an interesting point. However, wouldn't those groups just fine tune Kimi K3.1 pro no matter if it's nerfed or not, leaving you in the same position as before? That is, unless the nerf is easier to correct as compared to "upgrading" the models offensive capabilities. So a scenario where it is easy to "restore" offensive capabilities, but hard to "enhance" them beyond the labs best attempt. So is that the world we're living in? |
|
|
| |
| ▲ | ben_plotke 6 hours ago | parent | prev | next [-] | | > Seeing as no one besides blackhats want frontier cybercrime capability to be open source I'm not interested in black hat anything, but I am very invested in making sure the products I work on are not compromised. Given that state agencies have "frontier cybercrime capability", I would like to have the same. | | |
| ▲ | stalfie 3 hours ago | parent [-] | | I wrote a few lengthier comments on some other similar replies. Summarized my argument is that it seems to me to be strictly better that select defenders have an advantage, rather than everyone being equalized. If you're not one of the privileged few that might be frustrating, but open source models upgrade the attack and defense by the same amount, so open source cyber capabilities being at the frontier only results in a defender disadvantage. Replying here also as I'm curious about the counterargument. |
| |
| ▲ | LtdJorge 6 hours ago | parent | prev | next [-] | | It would also be very sensible to offer a BlackHat Pro version to national officials, for them. | |
| ▲ | CBLT 6 hours ago | parent | prev | next [-] | | Please don't change "cybersecurity" to "cybercrime" from one sentence to the next as a rhetorical flourish. It comes off as disingenuous and makes it harder to get your real point across. | | |
| ▲ | stalfie 3 hours ago | parent | next [-] | | Noted. I also did it intentionally to sound a bit spicy, which seemed like a good idea at the time. So I am guilty, and I regret my actions. | |
| ▲ | zozbot234 6 hours ago | parent | prev [-] | | "Cybersecurity" as a general term often includes offensive "cyber" which is what is being talked about here. | | |
| ▲ | bbg2401 4 hours ago | parent [-] | | But the person being addressed specifically used the term cybercrime. |
|
| |
| ▲ | verdverm 4 hours ago | parent | prev [-] | | Black Forest Labs did similar with vision capabilities https://bfl.ai/blog/capable-open-and-safe-combating-ai-misus... |
|
|
|
| ▲ | segmondy 7 hours ago | parent | prev | next [-] |
| They don't want to be banned, and maybe their best offensive cyber capability models will be for their govt. |
| |
|
| ▲ | Keyframe 4 hours ago | parent | prev | next [-] |
| We really need some breakthrough like DiLoCo does, but for heterogeneous unstable consumer hardware to make volunteer crowdsourced AI training a reality. Yeah, I understand from current technical angle how much of a mountain that is. Call it AI@Home or whatever. I never thought it would bother me personally or even become a problem, but these companies acting like gatekeepers and virtue signaling while also in bed with governments etc.. this leads nowhere good. |
| |
|
| ▲ | revolvingthrow 7 hours ago | parent | prev | next [-] |
| Yeah that's a huge downside. That the model does the task without tripping over its own feet, like discovering a vulnerability the model itself accidentally built 15 minutes ago and triggering its own guardrails, made the Chinese models attractive to use for security-adjacent things. Also useful to red-team your own stuff. While I can understand the reasoning behind it (and I guess having a model that's really good at both offense and defense released into the ether could lead to CCP asking some very pointed questions if Moonshot managed to get blamed for some incident stemming from their model's misuse) it's still a huge disappointment. I don't want to give US labs the results of my DNA tests and my family tree going back to the 16th century just to secure my shitty app, but if the Chinese are bowing out as well it seems the only alternative is to admit that some script kiddie with a bunch of tokens will just pwn you now and then. |
| |
| ▲ | arjie 6 hours ago | parent | next [-] | | If the Chinese want it, they have it. BGI does an enormous amount of sequencing. My own genome is entirely public (or was, and will be again when/if Personal Genome Project comes back) so you can watch and see if it harms me. | |
| ▲ | 0xWTF 7 hours ago | parent | prev [-] | | > I don't want to give US labs the results of my DNA tests My friend, you realize that if you have had blood drawn for a genetic test, there is a very decent probability that the sequencing was done by a Chinese lab operating in the US, right? The Chinese probably have more US genomes that the US does. https://pandorareport.org/the-gryphon-scientific-biosecurity... Also, illumina used to ship products with hardcoded S3 access, so purchasers of used equipment could gain access to sequencing information generated by the original owners. Too many links to cover all of it, here's the Gemini summary: https://share.google/aimode/4JLsHpeRCWlVqU8qT | | |
|
|
| ▲ | emilsedgh 5 hours ago | parent | prev | next [-] |
| Isn't this done so they can defuse Anthropic's excuse for regulatory capture? |
| |
|
| ▲ | Mattwmaster58 7 hours ago | parent | prev | next [-] |
| This doesn't seem particularly notable and is in line with Anthropic and OpenAI's approach of restricting release/access to more capable models. |
| |
| ▲ | _factor 7 hours ago | parent [-] | | It is notable in that it’s the first time an open Chinese company openly stated they were reducing intelligence for “safety”. “Our lock can be picked by the robot.”
We ban the robot instead of fixing the lock. It’s shortsighted. | | |
| ▲ | JoshTriplett 6 hours ago | parent | next [-] | | If we had a technique that would defeat almost every lock in the world, we might be prudent to delay releasing that until people have had time to change the locks. Same general benefit as coordinated disclosure, except it's a big game-theory problem where we're likely to eventually have sufficiently capable defectors. | |
| ▲ | senderista an hour ago | parent | prev | next [-] | | They are directly responding to new Chinese export controls on cyber capabilities. | |
| ▲ | vikramkr 5 hours ago | parent | prev [-] | | they're pretty clearly framing it as holding back on the robot and letting is lose slowly to give everyone time to update their locks |
|
|
|
| ▲ | grafmax 2 hours ago | parent | prev | next [-] |
| I hope one day they learn to inhabit their position more confidently instead of merely aping their competitors. |
|
| ▲ | baq 5 hours ago | parent | prev | next [-] |
| Read this as ‘dear government we can train a cyberweapon if you pay us’ assuming they wouldn’t say anything if they were already paid to do that |
|
| ▲ | modeless 5 hours ago | parent | prev | next [-] |
| They will. Just not in the version they release to you. |
|
| ▲ | comeonbro 6 hours ago | parent | prev | next [-] |
| Moonshot (Kimi) seems to be unashamedly into American culture[0], I wonder if they're paying closer attention to and giving more credence to some cultural aspects of American AI discourse including aspects of AI caution/panic. [0] https://x.com/crystalsssup/status/1944287779896328668 (note: extremely speculative and based on almost nothing, and especially near-complete ignorance to alternatives) |
| |
| ▲ | noelsusman 6 hours ago | parent [-] | | This is an extreme stretch before you even get into the fact that Pink Floyd is famously not American. | | |
| ▲ | TacticalCoder 4 hours ago | parent | next [-] | | And Radiohead ain't american either. Maybe GP meant to say that the model was westernized. | |
| ▲ | comeonbro 6 hours ago | parent | prev [-] | | [flagged] | | |
| ▲ | cromka 5 hours ago | parent [-] | | The American exceptionalism: even when it's not American, it still is. | | |
| ▲ | comeonbro 5 hours ago | parent [-] | | Unironically yes. | | |
| ▲ | locknitpicker 4 hours ago | parent | next [-] | | > Unironically yes. That just conveys an idea of being extremely desperate for being the leaders when you're clearly not it, and that despair is so great that you don't mind switching teams midway through just to be able to claim you're winning. | |
| ▲ | whoanoway 5 hours ago | parent | prev [-] | | [dead] |
|
|
|
|
|
|
| ▲ | WarmWash 7 hours ago | parent | prev | next [-] |
| All it takes is one idiot who happens to have the resources to "pWm Teh Interwebs" to scare both the US and Chinese governments. |
|
| ▲ | Onavo 7 hours ago | parent | prev | next [-] |
| The more interesting question is how much more performance can be squeezed out by post training the open weights through RL. |
|
| ▲ | TrainedMonkey 7 hours ago | parent | prev | next [-] |
| On the surface that seems like a responsible thing to do |
|
| ▲ | quotemstr 3 hours ago | parent | prev | next [-] |
| Cowards. The way to stop the vulnerability apocalypse is to fix the vulnerabilities, not to shoot the damn messengers. I hope someone abliterates and FTs this model on vulnerability discovery so we can find more bugs in our testing, insecure tech stacks. |
|
| ▲ | pcarolan 3 hours ago | parent | prev | next [-] |
| Good point. Wouldn't be good if there were white hat models being developed by legitimate organizations at this point? |
|
| ▲ | MisterMunchkin 5 hours ago | parent | prev | next [-] |
| Oh great, more censorship. We wouldn’t want those pesky plebs securing their work. |
|
| ▲ | woadwarrior01 6 hours ago | parent | prev | next [-] |
| Kimi is the closest Chinese equivalent of Anthropic. |
| |
|
| ▲ | ls612 6 hours ago | parent | prev | next [-] |
| I mean they say they will release the weights by November 4, so presumably after that it won’t be hard for people to fine-tune it to be better at cyber right? |
| |
| ▲ | lisplist 5 hours ago | parent [-] | | My understanding is if something is entirely absent from the dataset, good luck trying to teach a model that through post training | | |
| ▲ | efromvt 5 hours ago | parent | next [-] | | Given that most of their improvements here are positioned as RL on their last base train, seems like just doing some additional RL would work fine? | |
| ▲ | ls612 5 hours ago | parent | prev [-] | | Presumably if it knows how to find and fix bugs it can be told how to exploit them. But who knows what it will actually be capable of doing in the real world as opposed to Kiki’s benchmarks |
|
|
|
| ▲ | ex1fm3ta 5 hours ago | parent | prev | next [-] |
| [flagged] |
|
| ▲ | zozbot234 6 hours ago | parent | prev [-] |
| It's not actively nerfed like the Western frontier models, it's just downweighting offensive "cyber" as a domain for post-training/fine tuning. Which, if anything, ought to improve model capabilities wrt. other domains. |