| ▲ | l0new0lf-G 5 hours ago | ||||||||||||||||
How much hardware and even software that is supposedly used for encryption is actually backdoored? We know that Microsoft's bitlocker had at least one backdoor. Lenovo's fingerprint USB also has backdoors. It seems like only open source solutions actually provide encryption, like LUKS and Veracrypt. Then again, who guarantees that the executables are actually build from the source? Or that the keys aren't somehow sent over to agencies by the operating system? TLDR, we cannot realistically trust anything in this dictatorship of mass surveillance. | |||||||||||||||||
| ▲ | gruez 5 hours ago | parent [-] | ||||||||||||||||
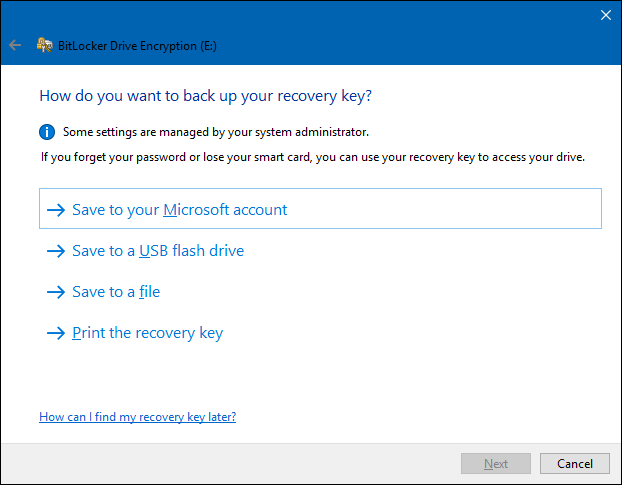
>We know that Microsoft's bitlocker had at least one backdoor Source? The closest I found was microsoft's key escrow system, but that's hardly a "backdoor" given it's publicly documented, and it's explicitly stated in no uncertain terms when you're setting it up[1] [1] https://static0.howtogeekimages.com/wordpress/wp-content/upl... | |||||||||||||||||
| |||||||||||||||||